Updated on
Microsoft 365 (Account-Level Emails)
Enabling the Microsoft 365 integration in SELMA allows you to use your organisation's Microsoft mailbox(es) to send emails directly from SELMA. Emails…
Enabling the Microsoft 365 integration in SELMA allows you to use your organisation's Microsoft mailbox(es) to send emails directly from SELMA. Emails sent within SELMA are also stored in the mailbox's Sent folder.
Note: Individuals with administrator access to your Microsoft tenancy should follow the steps below.
In this Section:
Setting up the integration involves four stages:
- Stage 1 — Register an Application in Microsoft Entra
- Stage 2 — Add a Client Secret
- Stage 3 — Configure API Permissions
- Stage 4 — Connect the Integration in SELMA
- Set-Up Complete
- Two-Way Communications
Stage 1 — Register an Application in Microsoft Entra
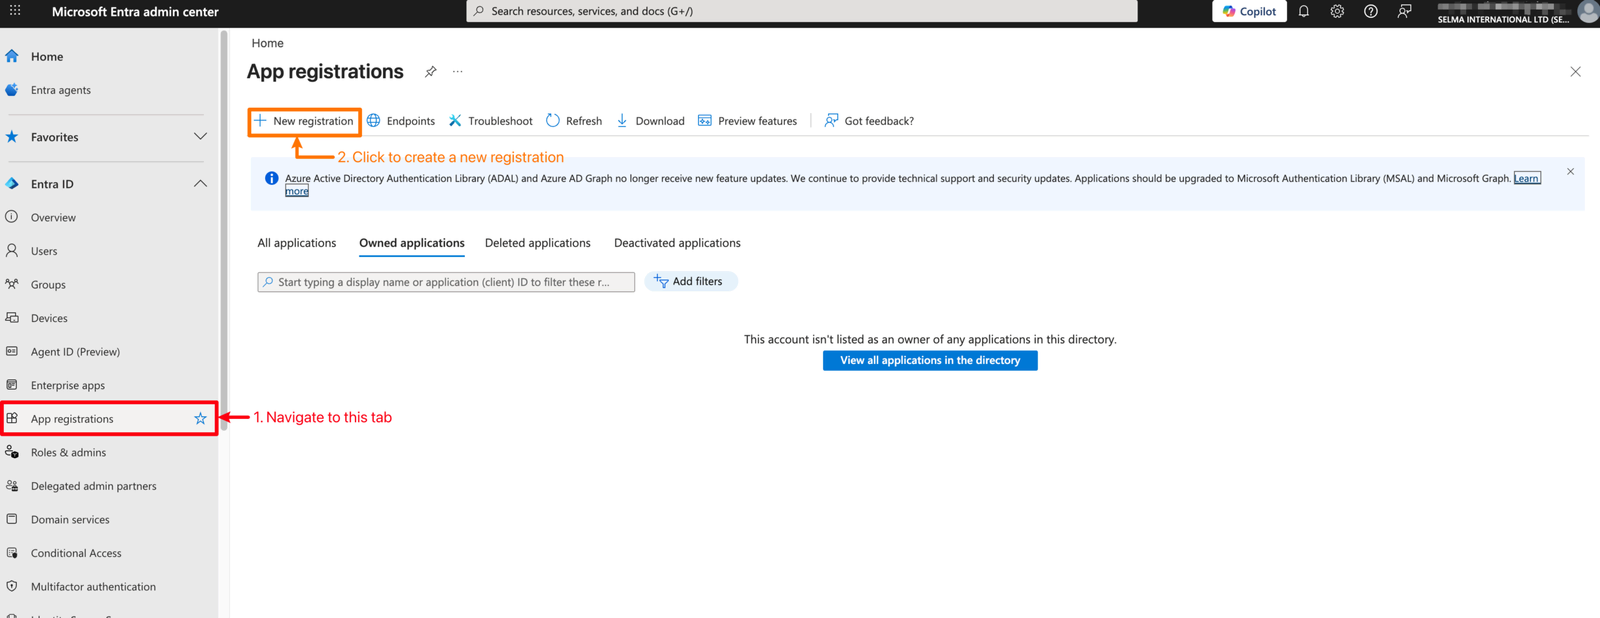
Go to the Microsoft Entra portal homepage: https://entra.microsoft.com/#home
Then, add a new registration.
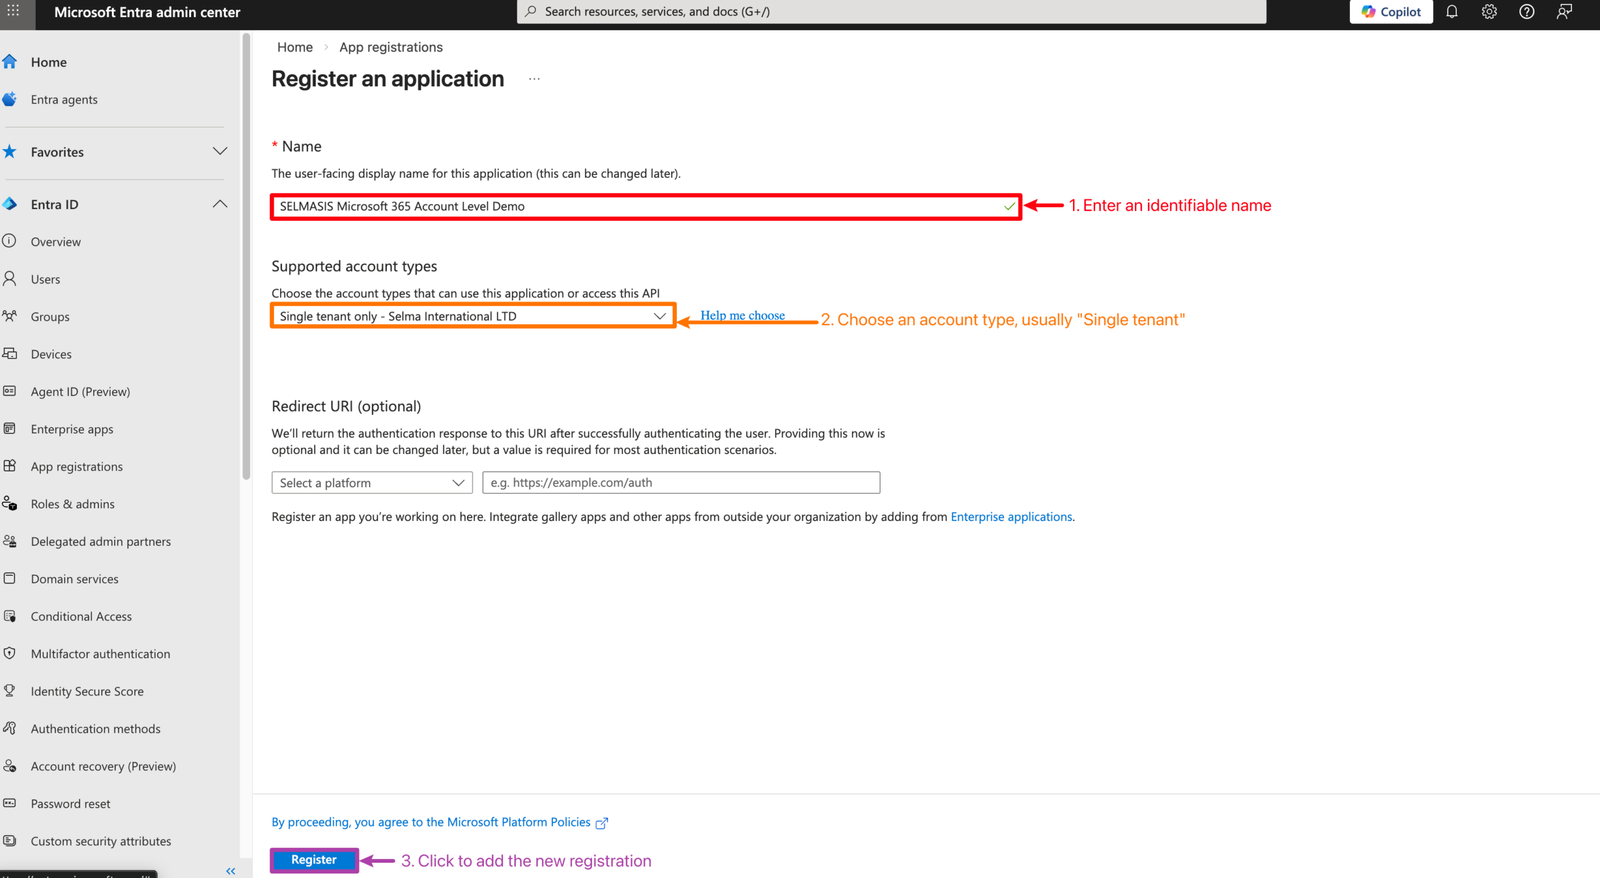
Name the application something identifiable, such as "SELMA M365 Integration". All remaining fields can be left at their default values. Click Register.
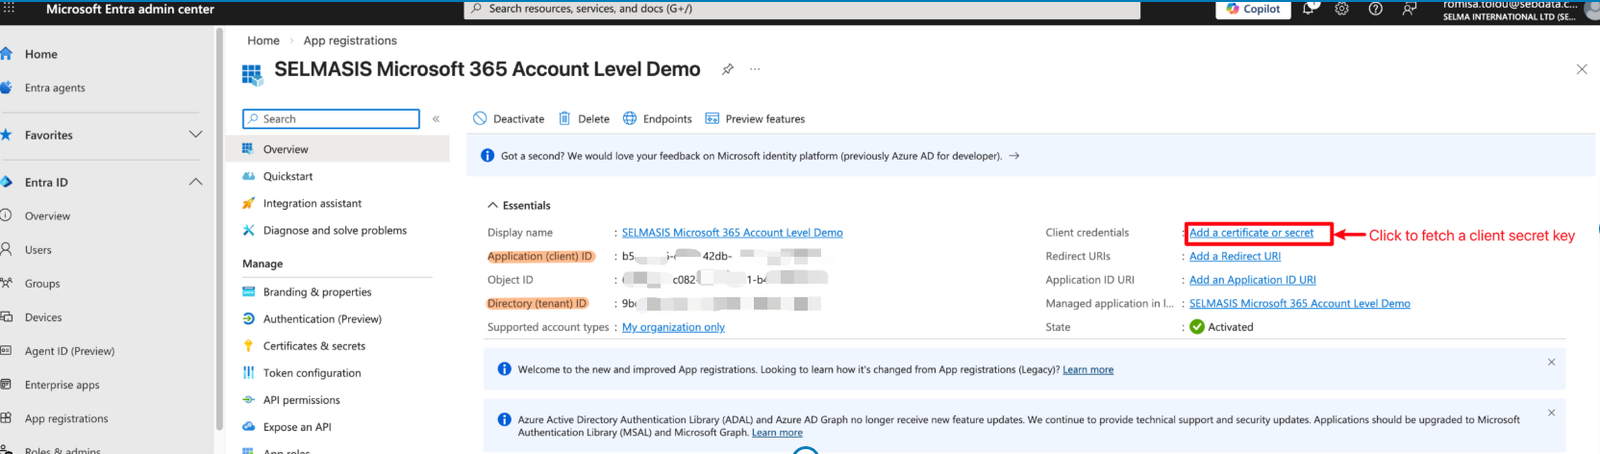
Once you have added a new registration, you will be taken back to the App Overview page, where you should note the Application (client) ID and Directory (tenant) ID. You will need these in Stage 4. Note: you will need to fetch a client secret key (red), which will be explained further in the next step.
Stage 2 — Add a Client Secret
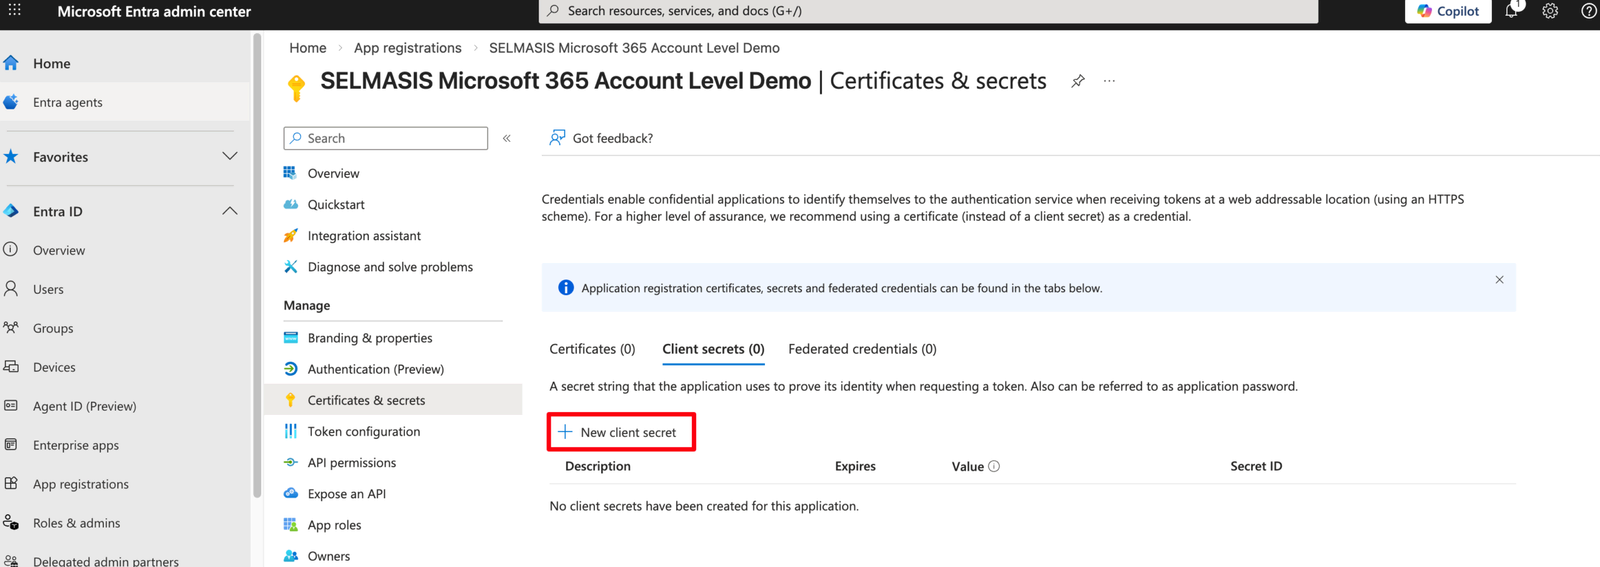
Click the button "+ New client secret". Note: You will have reached this page from the last step.
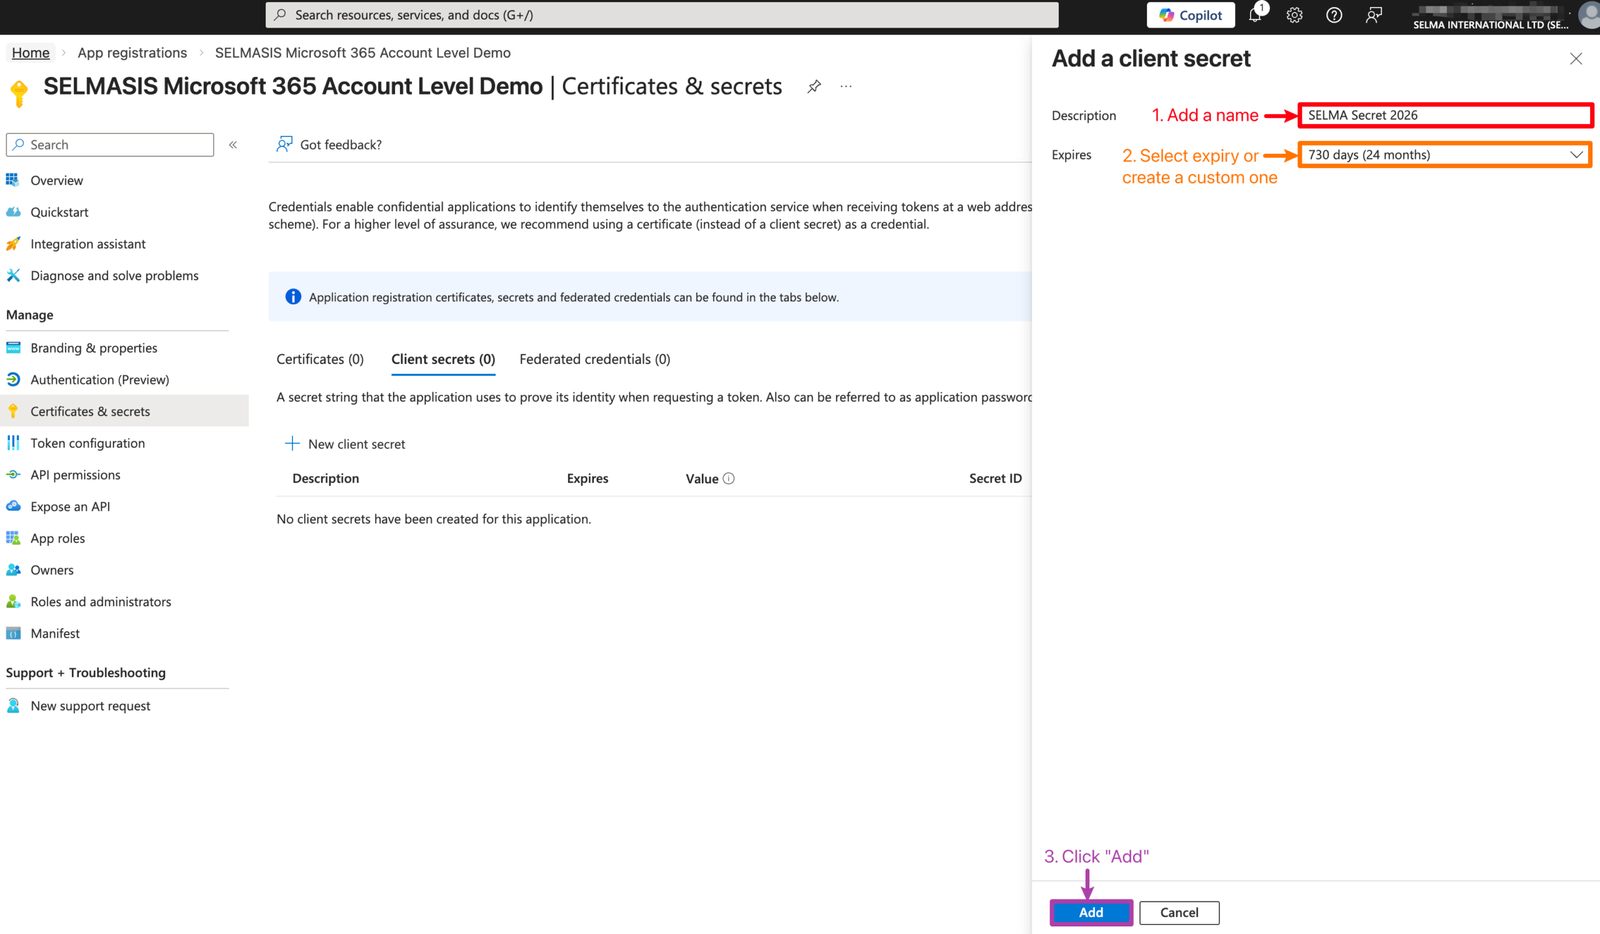
Enter a name and set an expiry duration, then click Add. ⚠️ Important: Set a reminder to create a new secret before it expires. Update the secret in SELMA before the expiry date to avoid any disruption.
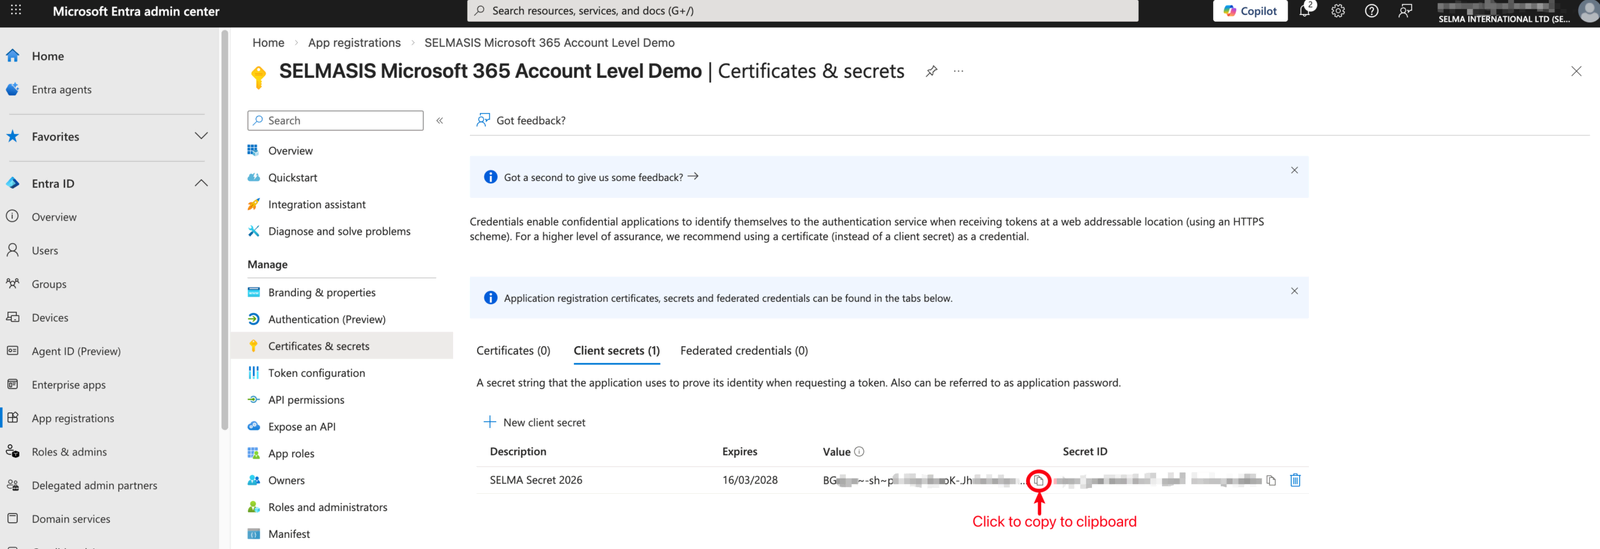
Copy the secret value immediately — it will not be displayed again after you navigate away or refresh the page. You will need this value in Stage 4. Note: If you can no longer copy the secret value, delete it and repeat Stage 2 from the beginning.
Stage 3 — Configure API Permissions
Within the same app, click API Permissions → Add a permission → Microsoft Graph.
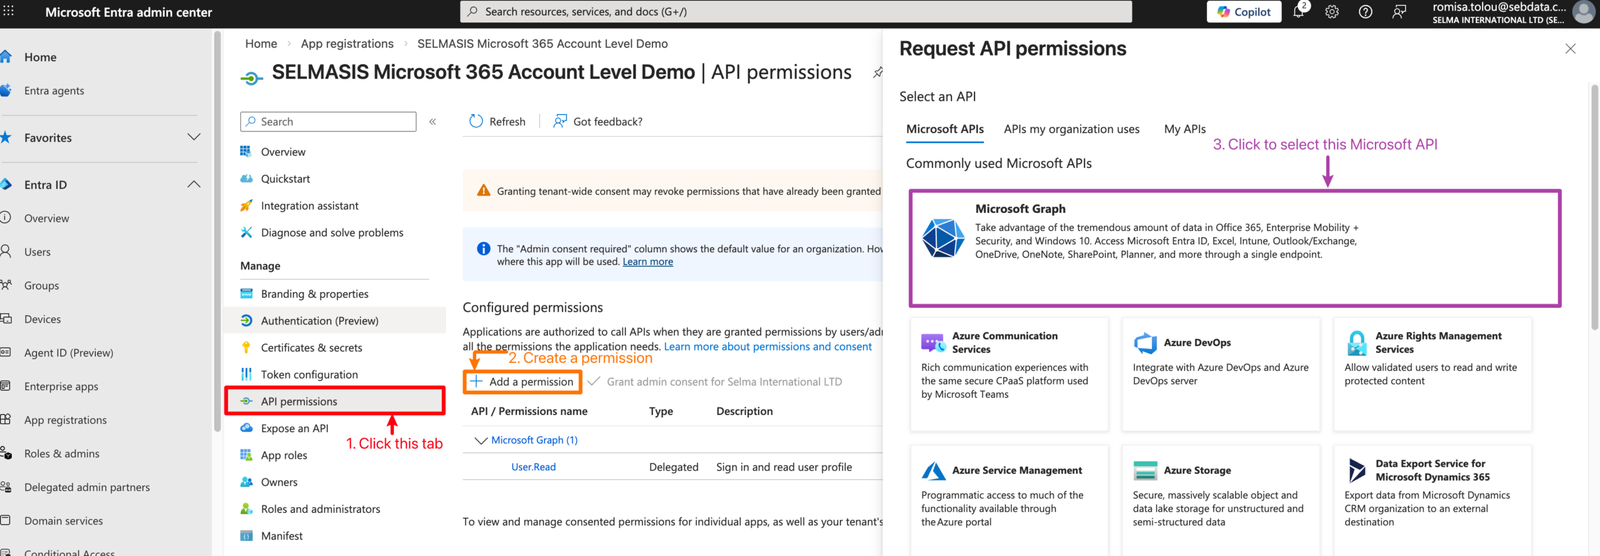
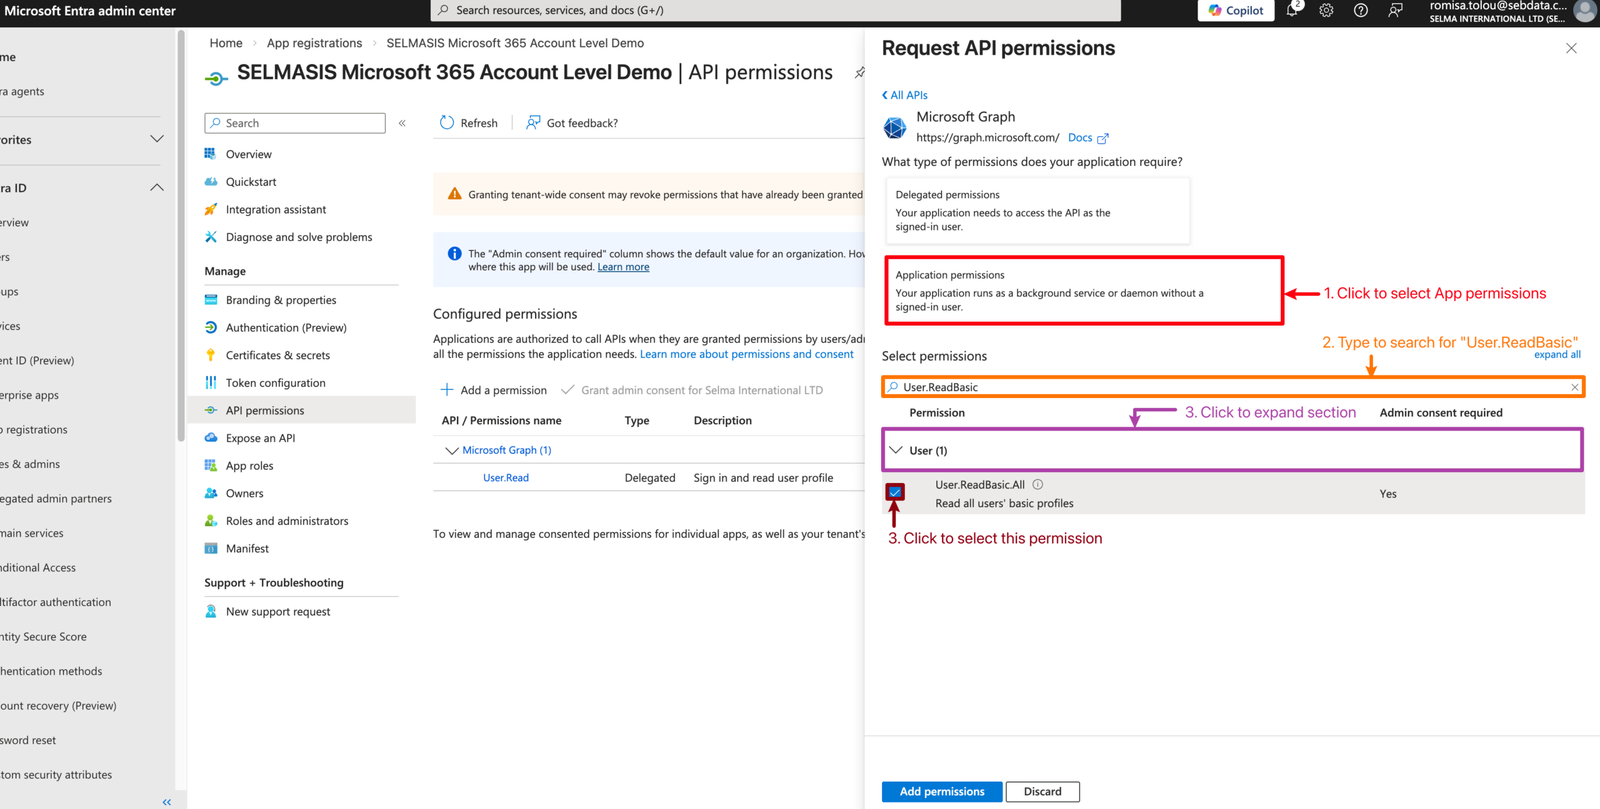
Select Application permissions (this allows the integration to send emails on the users behalf). Then, search for and add User.ReadBasic.All permission. This validates access to your designated mailbox.
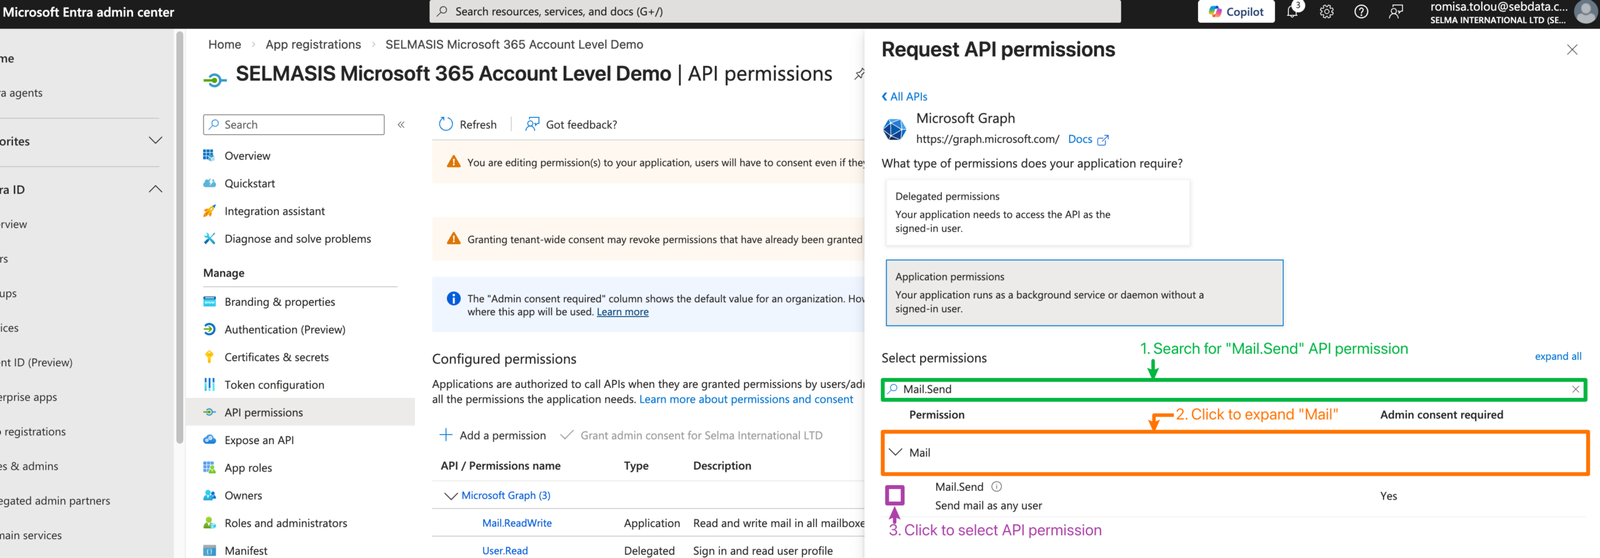
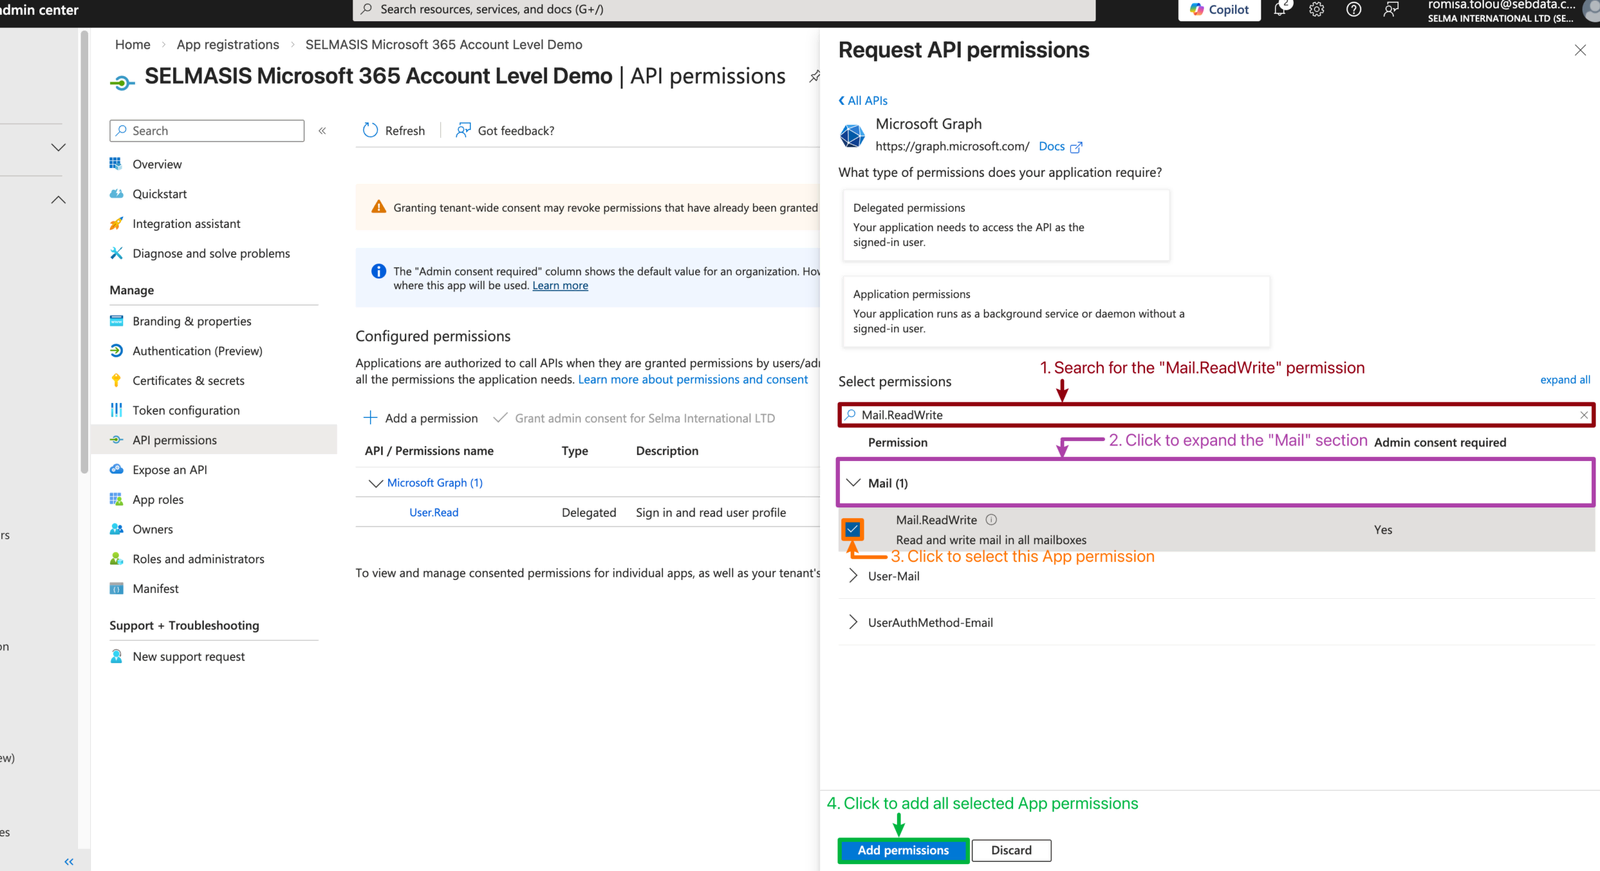
Search for and add the Mail.ReadWrite permission. This enables replies to emails leaving SELMA to appear in SELMA. Finally, add all permissions (green).
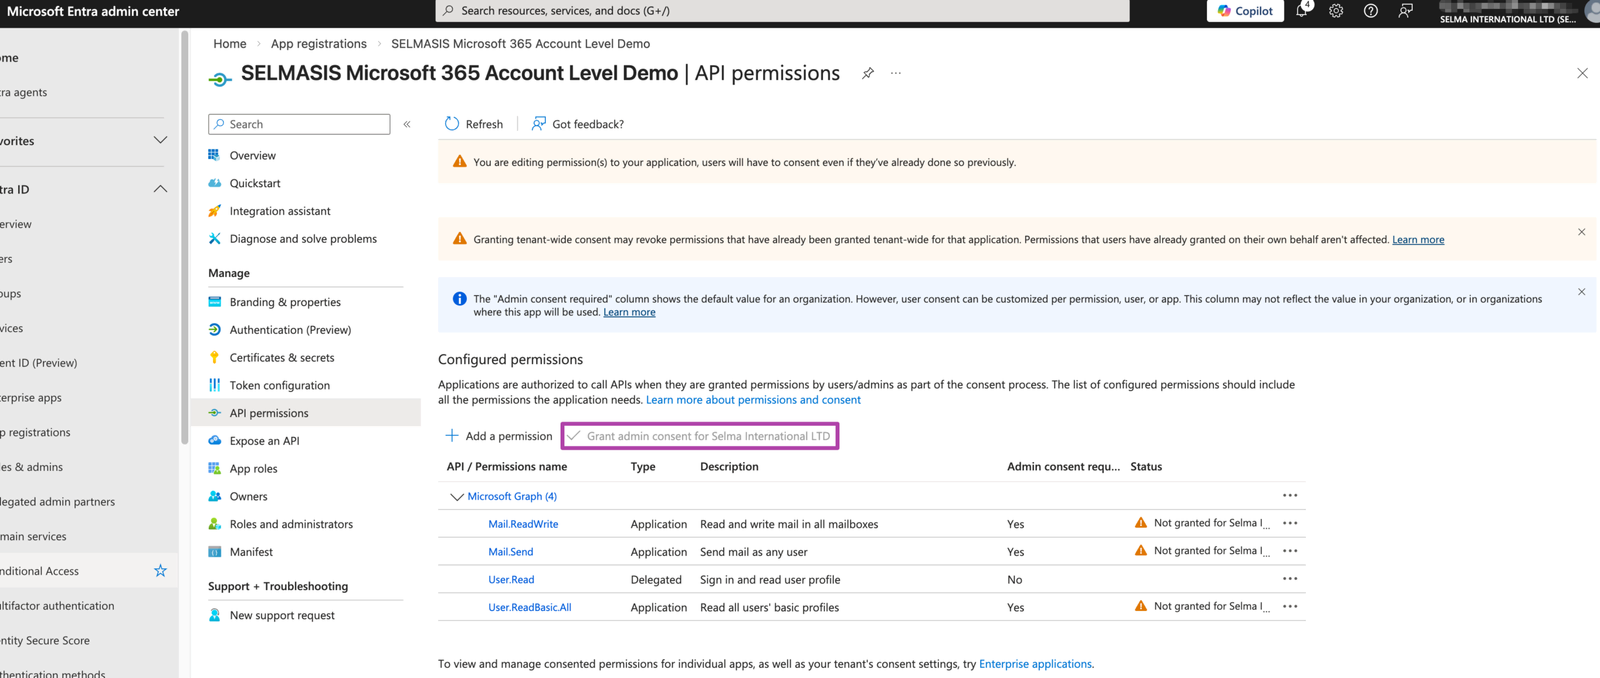
Once all permissions are added, click Grant admin consent to approve them for your organisation. Note: You will only be able to click this button if you are an admin or have the correct permissions, which is managed by your IT team.
Stage 4 — Connect the Integration in SELMA
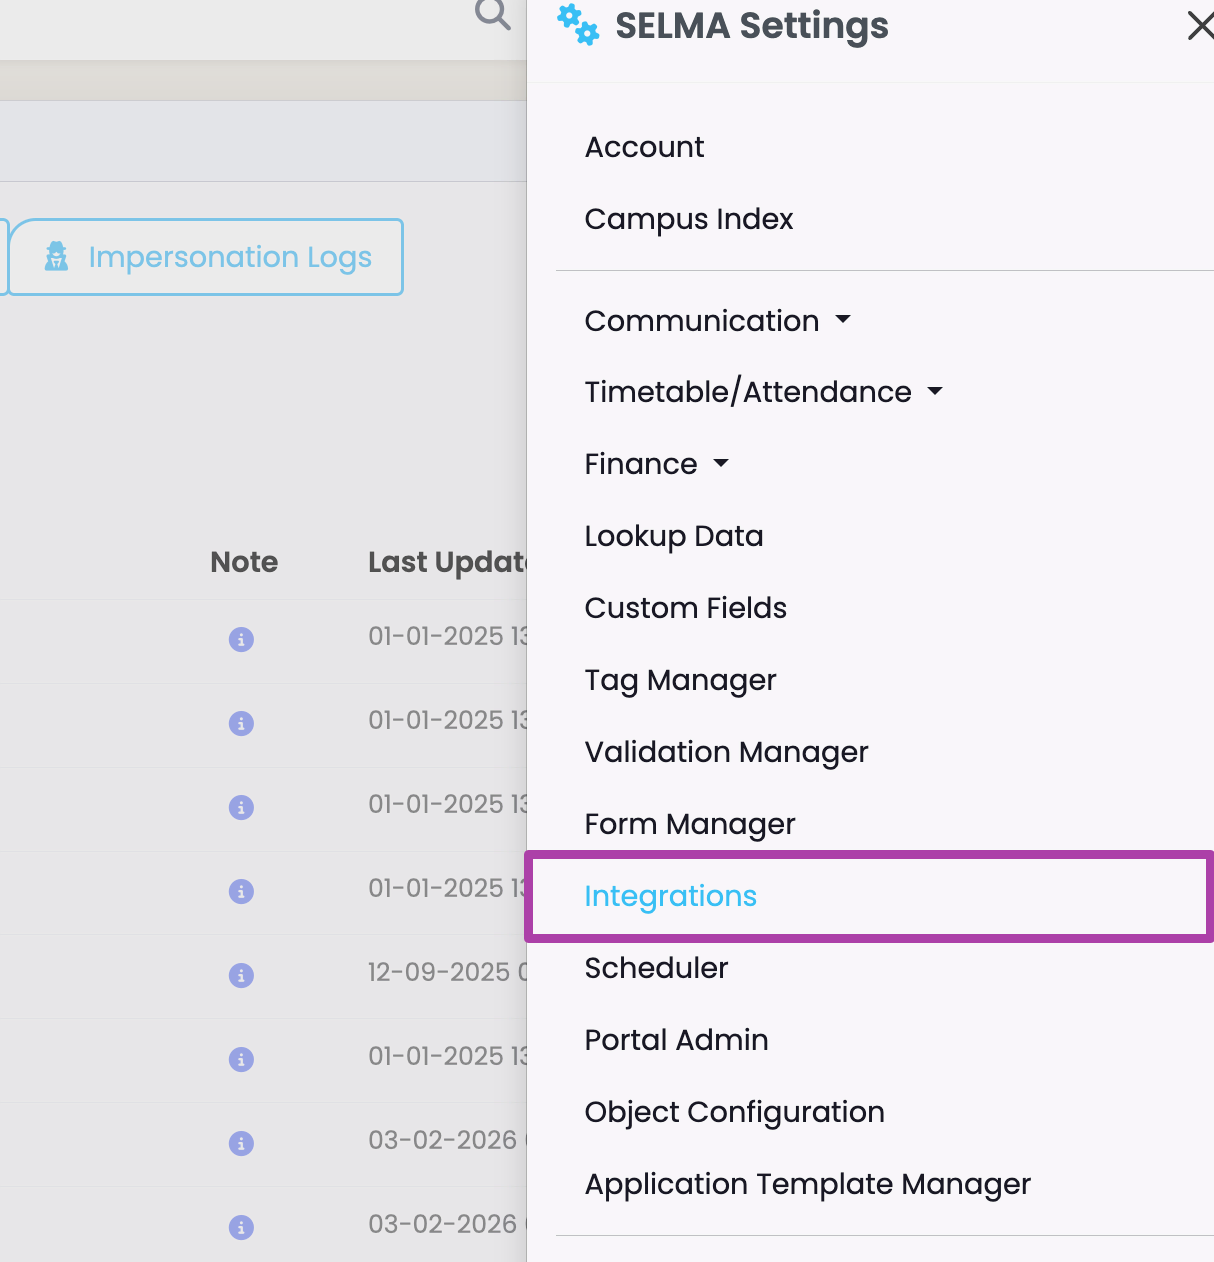
On your SELMA instance, go navigate to Settings (cog icon, top-right) > Integrations.
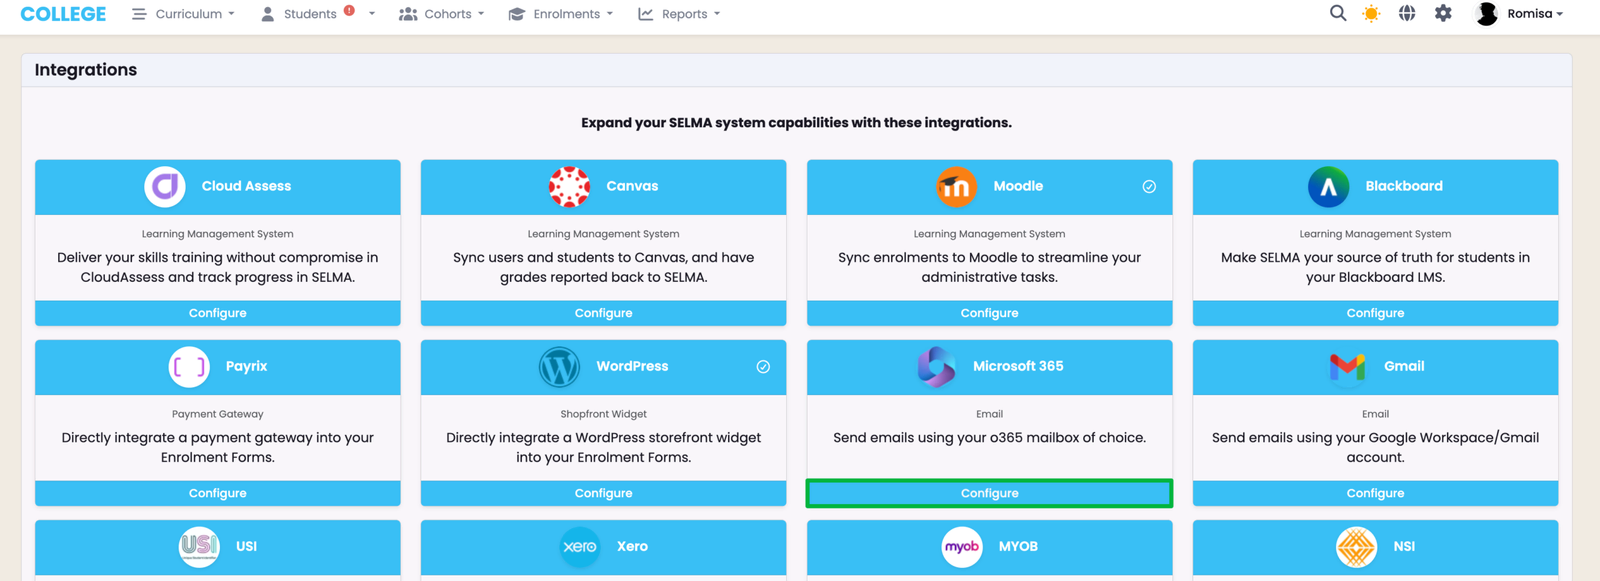
Click the "Configure" button, below Microsoft 365.
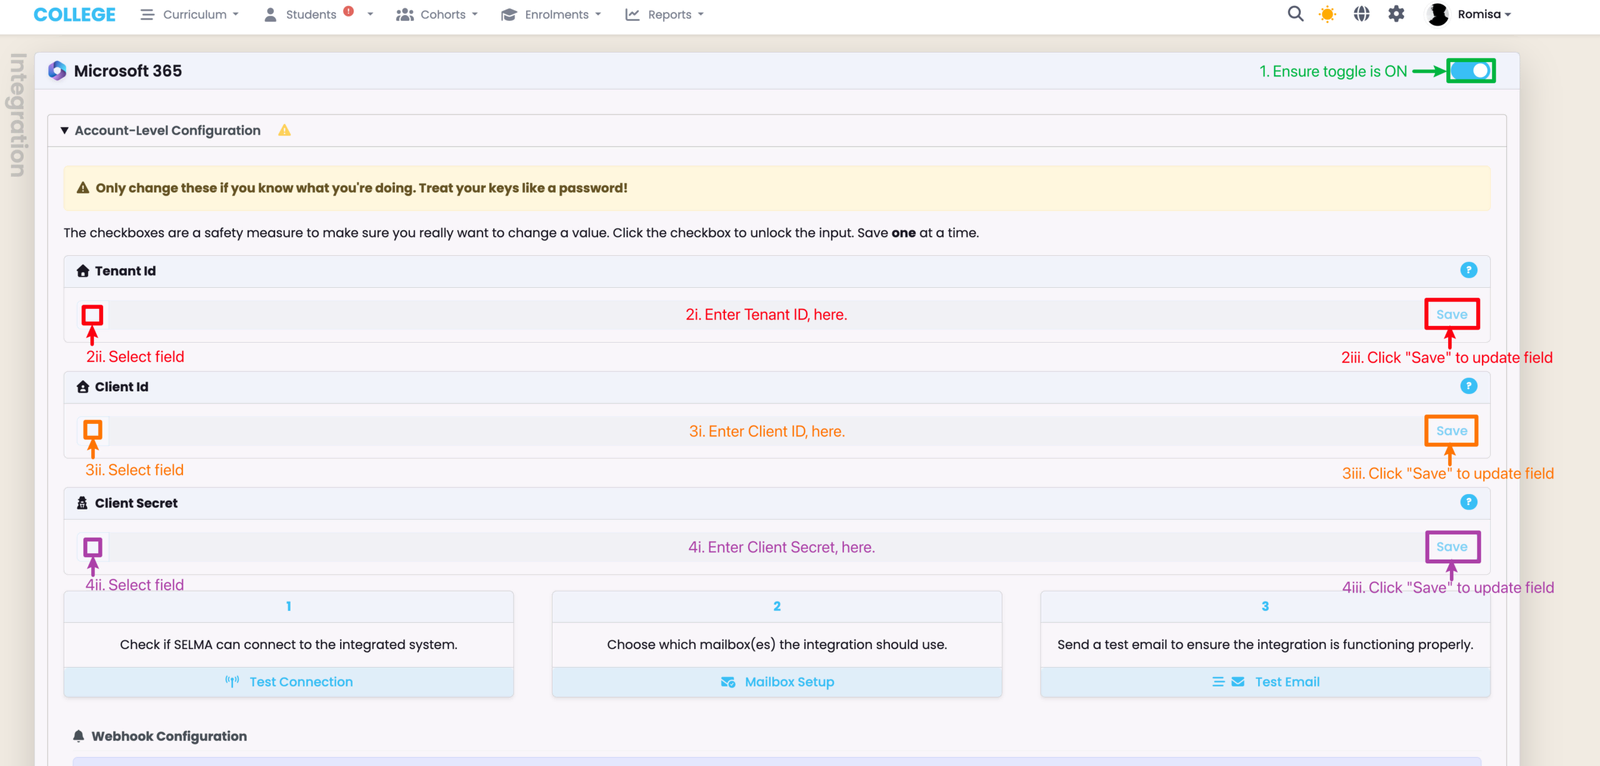
Expand the Account-Level Configuration section and enter the three values saved from Stages 1 and 2: Tenant ID and Client ID - Figure 1iii, and Client Secret Key - Figure 2iii.
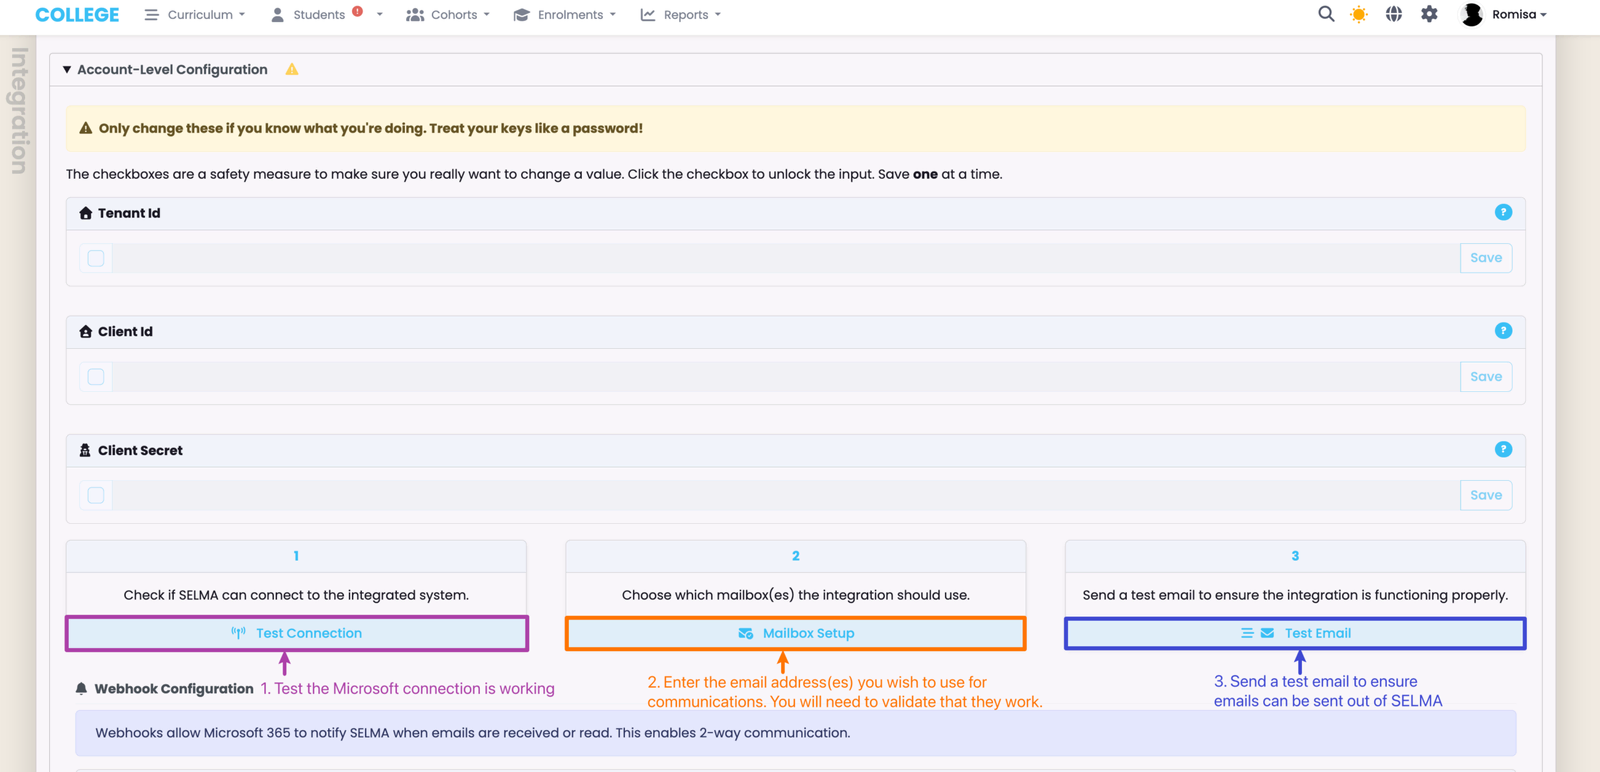
Test the connection to confirm the credentials are valid.
Then, click the Mailbox Set-up to enter and validate the email address(es) you wish to send communications from in SELMA.
Wish to limit the integration App's mailbox access in your Microsoft tenancy? Follow these steps
Finally, send a test email to confirm everything is working end-to-end. Note: If any of the tests and validations fail, please enquire with SELMA Support.
Set-Up Complete
The integration is now fully configured. This means you can send emails within SELMA from your validated mailbox address.
Two-Way Communications
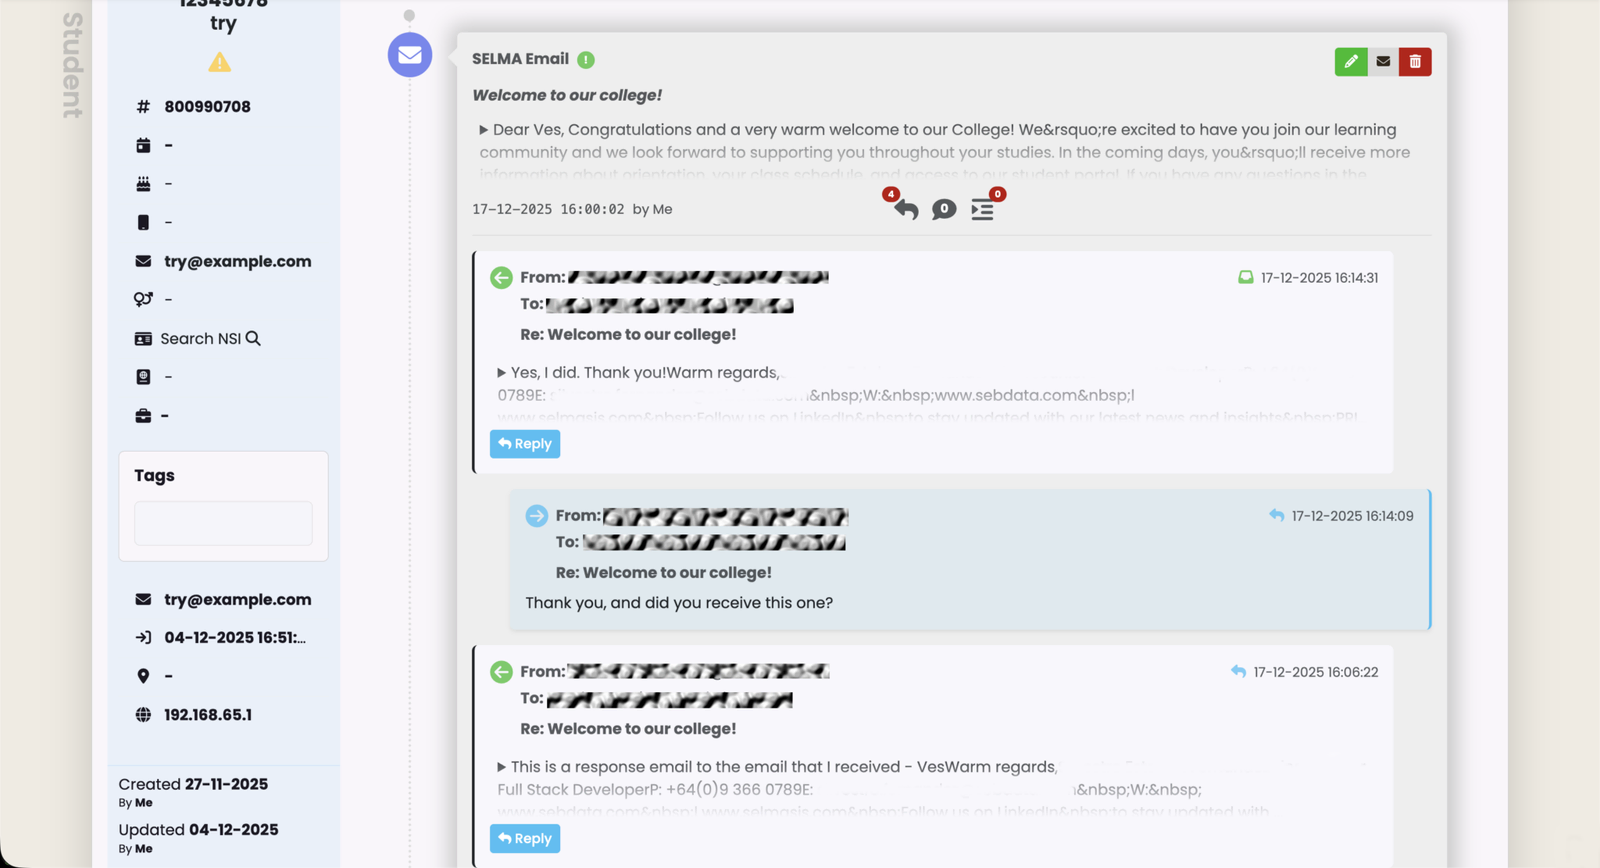
This feature allows you to see an email thread of correspondence within SELMA, which can be accessed from the Student Profile > Events tab.
- Please contact SELMA Support to enable this feature as part of your Microsoft Integration Plan.
Last updated
Login to SELMA with Microsoft
Enabling the Microsoft login in SELMA allows users to authenticate themselves, using their Microsoft accounts. This improves the User Experience by…
Microsoft 365 (User-Level Emails)
Enabling the Microsoft 365 integration in SELMA allows you to use your organisation's Microsoft mailbox(es) to send emails directly from SELMA. Emails…